PentAGI: Autonomous Multi-Agent AI Penetration Testing Guide
PentAGI: autonomous multi-agent AI penetration testing platform (vxcontrol/pentagi). Orchestrate Kali Linux tools in Docker to discover and exploit flaws.
TL;DR
Quick Answer Box (Google Search Featured Snippet):
- What is PentAGI? PentAGI is an open-source autonomous multi-agent penetration testing platform (
vxcontrol/pentagi) that bundles 20+ Kali Linux security tools (nmap,sqlmap,metasploit,hydra) in isolated Docker sandboxes to autonomously discover, exploit, and verify security vulnerabilities.- How does PentAGI differ from traditional vulnerability scanners? Traditional scanners generate noisy false-positive PDFs; PentAGI coordinates specialized AI subagents (Researcher, Developer, Executor) with persistent dual-memory (Neo4j Graphiti + PostgreSQL pgvector) to execute reproducible proof-of-concept (PoC) exploits.
- Quick Start: Clone the repository
git clone https://github.com/vxcontrol/pentagi, rundocker compose up -d, and launch an automated audit through the web UI or API.- Official Repository: vxcontrol/pentagi on GitHub.
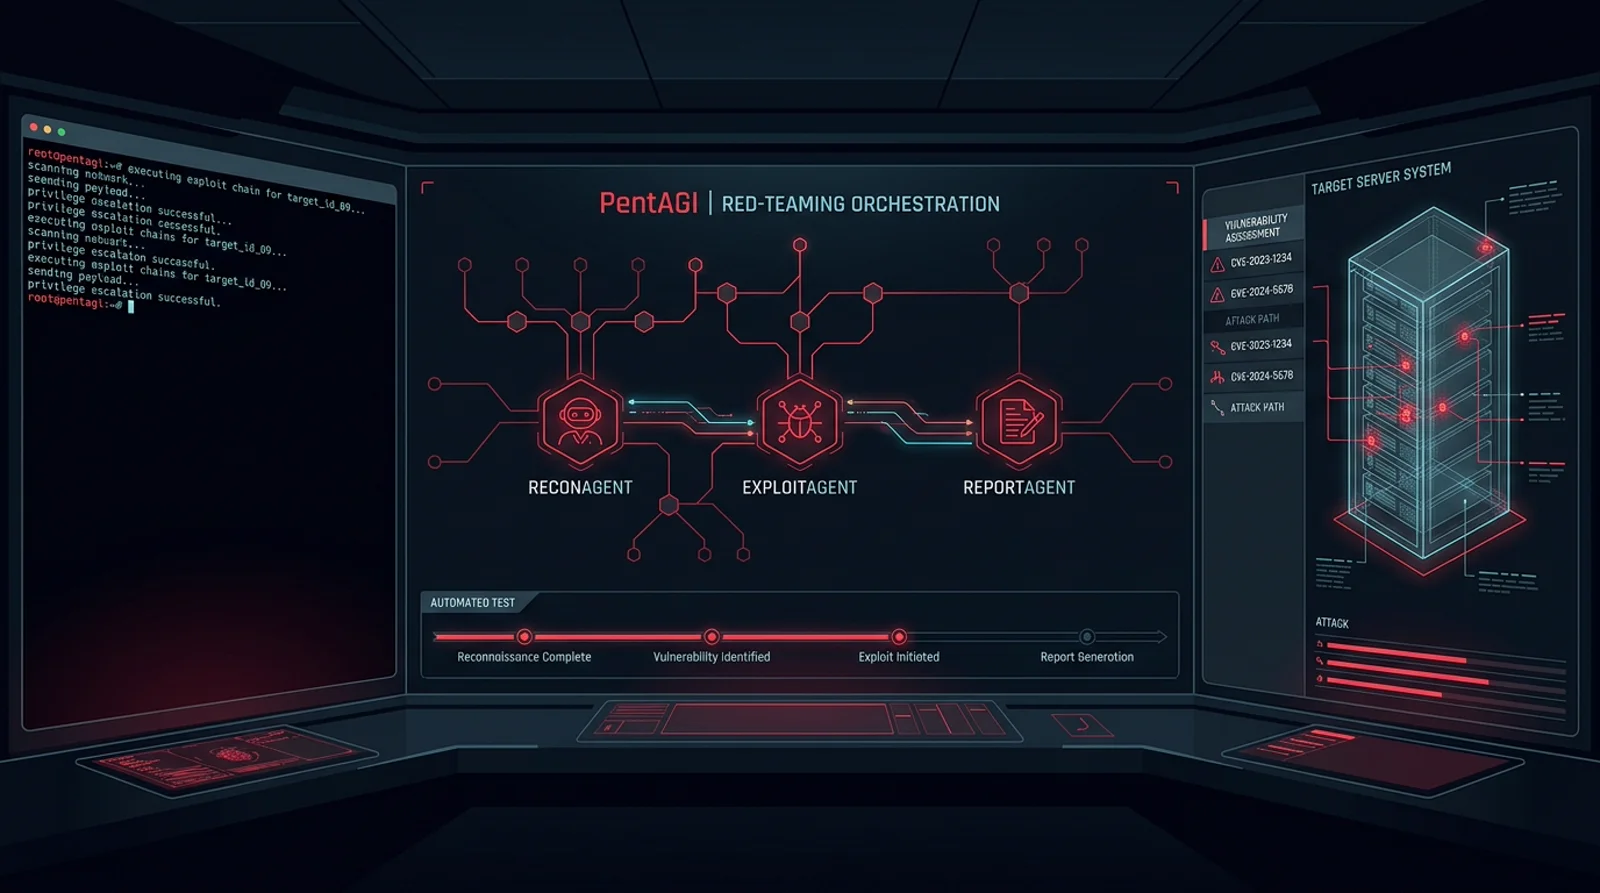
Standard security scanners spit out hundreds of passive warnings, but PentAGI actually exploits them autonomously. It bundles Kali-grade offensive CLI tools (nmap, sqlmap, metasploit) inside isolated Docker containers, coordinates specialized subagents (Researcher, Developer, Executor), and uses a dual-memory layer (Neo4j Graphiti plus PostgreSQL pgvector) so the agent never loses context during hours-long penetration tests.
Beginner Map: The 4-Layer Autonomous Pentesting Stack
The 3-Minute Fast Path: Launch Your First Autonomous Pentest
- Spin Up Stack: Clone
vxcontrol/pentagiand rundocker compose up -dto launch the orchestrator and sandboxed Kali daemon. - Configure Target Scope: Define target IP or domain and set offensive boundaries in the web dashboard.
- Dispatch Multi-Agent Squad: The Researcher subagent runs non-invasive reconnaissance (
nmap, subdomains), while the Developer agent writes custom exploitation scripts. - Inspect Verified Proof-of-Concept: Review validated exploit traces without false positives. Compare with Strix for developer-friendly CI/CD security agents and Shannon for architectural penetration testing.
Before looking at Go daemons and GraphQL payloads, understand how PentAGI differs from single-prompt LLM scripts:
| Layer | Component | Responsibility |
|---|---|---|
| 1. Brain | Multi-Agent Orchestrator | Splits high-level goals into targeted attack phases across Researcher, Developer, and Executor agents. |
| 2. Memory | Graphiti (Neo4j) + pgvector |
Maps infrastructure topology and recalls prior successful attack vectors without token bloat. |
| 3. Muscles | Sandboxed Docker Kali Tools | Safely runs real CLI binaries (nmap, sqlmap, hydra) without exposing host networks. |
| 4. Nervous System | OpenTelemetry + Langfuse | Traces LLM calls, latency spikes, and automated vulnerability reports in real time. |
Part 1: Foundations (The Mental Model)
Think of standard security scanners like a spell-checker. They look for known bad patterns (like outdated dependencies or missing headers) and dump an overwhelming PDF list of warnings.
PentAGI, on the other hand, is like hiring an entire team of offensive security engineers.
When you point it at a target, it does not just scan:
- Researches the target’s footprint using external web search and scrapers.
- Plans an attack using a developer agent that understands 20+ professional tools (like
nmap,sqlmap,metasploit). - Executes the attacks, adapts if blocked by a firewall, and remembers what worked for the next step.
- Reports the exact exploitation guide with verified curl reproduction steps.
The Mental Model: PentAGI = Multi-Agent AI System + Sandboxed Kali Linux Tooling + Persistent Memory Graph.
Similar to how OpenSandbox isolates arbitrary agent code and Pi-Mono builds single-binary agent loops, PentAGI treats security tooling as isolated capability modules.
Part 2: The Investigation
Under the hood, PentAGI is a marvel of modern microservices architecture, heavily utilizing Go, PostgreSQL, and Graph databases.
Here are the core architectural pillars:
- The Brain (Multi-Agent System): An orchestrator dividing tasks between a Researcher, a Developer, and an Executor.
- The Memory (Graphiti & pgvector): This is the architectural breakthrough. PentAGI uses a Neo4j-powered Knowledge Graph (Graphiti) to store relationships between entities (e.g., this endpoint uses this DB, which is vulnerable to this CVE). It also uses PostgreSQL with
pgvectorto remember past successful exploitation chains. - The Muscles (Isolated Tools): The system connects to a sandboxed Docker environment where commands are executed safely.
- The Nervous System (Observability): Built-in logging with OpenTelemetry, Grafana, Jaeger, and LLM specific analytics via Langfuse.
Crucially, it is completely model-agnostic. You can plug in OpenAI, Anthropic, Gemini, AWS Bedrock, or local models via Ollama.
Part 3: The Diagnosis
What does this mean for backend and web developers?
Usually, pentesting is an external process done right before launch. PentAGI’s comprehensive APIs (REST and GraphQL) allow you to integrate autonomous red-teaming directly into your CI/CD Pipelines with GitHub Actions.
Real Use-Case: The CI/CD Web Pentest
Instead of just running static unit tests, you can trigger an autonomous agent in your deployment workflow to perform automated red-team audits against your staging environment.
Behind the scenes, the agent follows strict heuristic prompts, such as checking specific web layers. Here is how PentAGI instructs its agents internally to do a full Web Application Pentest:
# 1. Collect All Endpoints of the Application
Navigate through pages, document exact URLs, inputs, and file upload endpoints.

# 2. Perform Checks on Inputs
- Path Traversal: Read /etc/passwd on Linux targets
- CSRF: Convert POST to GET, test without tokens
- XSS: Inject unique strings like XSS_TEST_123, bypass filters
- SQLi: Map inputs and run sqlmap with tamper scripts
- Command Injection: Use time-based payloads (e.g., `sleep 10`)
- SSRF: OOB interaction via Interactsh
Code Example: Triggering a Flow via GraphQL
Because PentAGI treats everything as a “Flow,” developers can programmatically kick off a pentest using a standard Bearer token:
curl -X POST https://your-pentagi-instance:8443/api/v1/graphql \
  -H "Authorization: Bearer YOUR_API_TOKEN" \
  -H "Content-Type: application/json" \
  -d '{
    "query": "mutation { createFlow(modelProvider: \"openai\", input: \"Test the security of https://staging.myapp.com focusing on SQLi on the search endpoint\") { id title status } }"
  }'
Handling Massive Context Windows
If you have built autonomous agents with OpenClaw or custom daemons, you know contexts get bloated quickly. PentAGI solves this natively through an AST-based Chain Summarization system. It intercepts oversized LLM pair messages, selectively summarizes earlier task history into pgvector (see our primer on Vector Databases & Embeddings), and keeps the immediate working memory fresh.
Student First Assignment
To understand how multi-agent coordination works without risking your production infrastructure, run this 15-minute hands-on drill:
- Deploy an intentionally vulnerable mock target: Run
docker run -d -p 8080:80 vulnerables/web-dvwaon your local bridge network. - Point PentAGI in restricted scope mode: Limit the target URL to
http://localhost:8080/vulnerabilities/sqli/and allow onlysqlmaptool access. - Inspect the Neo4j Graphiti console: Observe how the agent automatically registers the database type, injectable parameters, and payload attempts as distinct entity nodes.
- Export the reproducible curl artifact: Verify that the generated reproduction script succeeds against the local container with zero human assistance.
Part 4: The Resolution
Getting started is straightforward thanks to Docker Compose:
- Clone & Configure:
git clone https://github.com/vxcontrol/pentagi.git && cd pentagi
curl -o .env https://raw.githubusercontent.com/vxcontrol/pentagi/master/.env.example
(Add your API keys to the .env file, e.g., OPEN_AI_KEY or OLLAMA_SERVER_URL)
- Boot the Stack:
docker compose up -d- Interact: Head over to
localhost:8443for the UI, or hit the API playgrounds. You create a new Assistant, assign it an LLM, turn on “Agent Delegation,” and give it a mission.
A Word of Caution: PentAGI executes real exploits. Never point it at infrastructure you do not explicitly own or have written permission to test. Ensure it runs in a secured Docker network context.
Final Take
- Traditional Pentesting Tools: Manual, precise, but require a human to stitch findings together.
- PentAGI: An autonomous team in a box. It understands context, queries a knowledge graph of vulnerabilities, executes real CLI commands in a sandbox, and remembers what works using vector search.
- The Modern Shift: Pentesting is no longer an annual compliance ritual. By combining agent orchestration with container sandboxing, security testing becomes an automated gate just like linting or unit tests.
PentAGI Frequently Asked Questions (FAQ)
1. What is PentAGI and how does it differ from traditional scanners like Nessus?
Traditional scanners (like Nessus or Nikto) rely on static signature matching and heuristic fuzzing, generating massive lists of potential issues without validating them. PentAGI is an autonomous multi-agent system: it reasons about web architecture, combines 20+ offensive CLI tools (nmap, sqlmap, metasploit) inside isolated Docker containers, executes dynamic proof-of-concept exploits, and outputs reproducible reproduction commands.
2. Is PentAGI safe to run against staging or production systems?
PentAGI performs live offensive security exploitation and can alter database states or trigger denial-of-service conditions if run unconstrained. You must only run PentAGI in controlled staging or test environments with explicit authorization. Always configure strict execution boundaries, target scope whitelists, and read-only flags when evaluating live targets.
3. What models and local infrastructure does PentAGI require?
PentAGI is completely model-agnostic. It supports cloud providers (OpenAI GPT-4o, Anthropic Claude 3.5 Sonnet, Gemini 1.5 Pro) as well as locally hosted open-weights models through Ollama (e.g. Llama-3-70B, DeepSeek-Coder). For local execution, ensure your machine has at least 32GB RAM and an NVIDIA GPU with 16GB+ VRAM if running local inference models alongside Docker containers.
4. How does PentAGI prevent LLM context window overflow during long pentests?
PentAGI implements an AST-aware Chain Summarization engine combined with dual memory. It records infrastructure entities and exploit findings in Neo4j Graphiti, preserves execution traces in PostgreSQL pgvector, and prunes intermediate terminal stdout/stderr before tokens overflow the context window.
Related Architectural Deep Dives
- Pi Mono: Autonomous AI Coding Agent Architecture: Explore how single-binary agent loops coordinate deterministic CLI tools and file system manipulation.
- OpenSandbox: Secure Container Execution for Autonomous Agents: Discover how container isolation patterns protect host environments from arbitrary agent code execution.
- Omniroute: Dynamic LLM Gateway & Traffic Routing: Set up high-availability model fallbacks to prevent rate limits during long-running multi-agent penetration workflows.
Related posts
Strix: Open-Source Autonomous AI Pentesting & Security Agent Tool
Strix AI pentesting tool (usestrix/strix): autonomously discover, exploit, and prove security flaws in CI/CD pipelines with sandbox verification.
Shannon Explained: The Autonomous AI Pentester That Breaks Your App Before Hackers Do
Shannon by Keygraph is a fully autonomous AI penetration tester that executes real exploits - not just advice - across web apps and networks.
What AI DevKit is: a control plane for AI coding agents - and where it stops
An architectural guide to AI DevKit: local-first CLI/TUI console, shared config, SQLite memory, and workflow skills for managing multiple coding agents.
Free Claude Code Explained: One Local Proxy for 50+ AI Providers
Free Claude Code routes Claude Code, Codex, Pi, and eight more agents through one local proxy with 50 ToS-friendly providers and automatic fallback.