The Anatomy of a Disappearing Payload: Yellorn Lab Cross-Tab Handoff
How an obscure HTML Living Standard rule in window.open wiped cross-tab editor payloads on Yellorn Lab, and how we rewired ComfyUI default graph view.
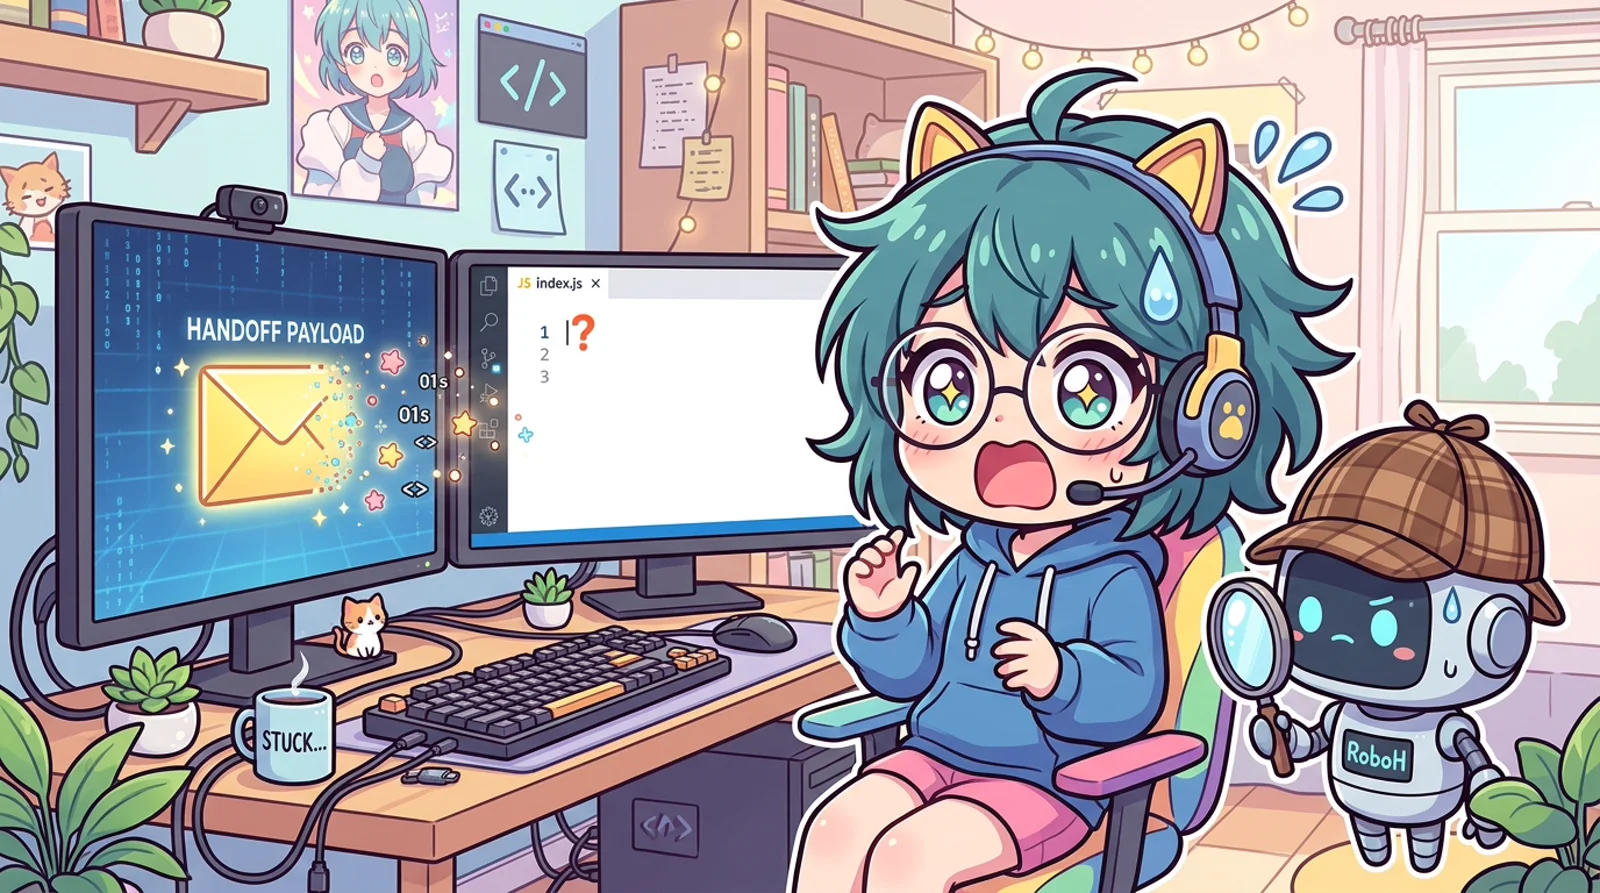
Picture this scenario: you just reproduced an intricate AI workflow on Yellorn Lab featuring Wan2.1 and nine chained LoRA sliders. You spot a prominent action button: “Open in Yellorn Editor (Inspect Graph)”. You click it, eager to examine the visual node canvas and trace how latent tensors, samplers, and prompts wire together.
A fresh browser tab pops open: yellorn.com/?handoff=handoff_17594.... You wait a brief second for React hydration. The editor layout mounts cleanly, but the canvas is completely blank. Zero nodes. Zero workflow graph. Not a single line of JSON inside the Monaco editor workspace. A structured 27KB payload vanished into thin air without leaving a trace.
What swallowed the payload between two browser tabs?
TL;DR
Quick Answer Box (Google Search Featured Snippet): What is the Yellorn Lab Cross-Tab Handoff Bug? It was an elusive payload loss incident during cross-tab workflow handoff triggered by the HTML Living Standard. Passing the
noopenerfeature flag causeswindow.opento returnnullby specification design, making defensive popup-detection code falsely assume the window was blocked and wipelocalStoragebefore the target tab could read it.
- The HTML Living Standard Trap: Specifying
"noopener"in window features forceswindow.opento returnnullto isolate browsing contexts. - False-Positive Popup Detection: Checking
if (!opened)wrongly flags legitimate popup launches as blocked, executing self-destructive cleanup code that deletes the pending ticket. - ComfyUI Graph-First Inversion: Reordering the format metadata declaration to
["graph", "tree"]so incoming workflows launch directly into the visual node canvas rather than a dry JSON inspector. - Lifecycle Hygiene: Automatically closing the blank initial tab and scrubbing
?handoff=from the URL bar immediately after consumption. - Repository: HoangYell/yellorn-com on GitHub (MIT License).
Beginner Map (Mental Model)
Think of cross-tab handoff like an automated locker at a post office: the sender deposits a package into a numbered compartment, sets a 30-second combination lock, and sends the ticket number to the receiver. But because the sender walked away immediately assuming the courier failed to arrive, they hit the locker emergency purge button, leaving the receiver staring into a clean empty steel box.

Part 1: Foundations (Mental Model)
Why bother with a cross-tab handoff protocol instead of passing data straight through URL search parameters? A production ComfyUI workflow JSON easily spans 20KB to 200KB, packing node graphs, custom widget states, latent dimensions, and positive prompts. Web browsers and reverse proxies choke on oversized query strings exceeding 2KB, triggering HTTP 414 URI Too Long errors and cluttering the browser navigation history.
To bridge state across tabs without hitting URL bounds, modern web applications rely on an ephemeral ticket handoff pattern. The sending tab generates a random ticket ID with an expiration window, writes the heavy data into browser local storage, and passes only the lightweight ticket ID across the URL boundary.
| Core Terminology | Plain English Definition (3-6 words) |
|---|---|
| LocalStorage | Browser-persisted client-side key-value store |
| Cross-Tab Handoff | Transferring application state between tabs |
| Reverse Tabnabbing | Exploit altering parent window location |
| WindowProxy | Browser wrapper representing window context |
| TTL (Time to Live) | Shelf life before automatic expiration |
Once the destination tab initializes, its mounting logic inspects the search parameters, extracts the ticket key, retrieves the payload from storage, and removes the entry to prevent storage pollution. On paper, this architecture is robust, predictable, and clean. That is, until it collides with web security specifications.
Part 2: Investigation (How It Works)
During headless browser forensics with Chrome DevTools Protocol, we observed an anomaly: when the target editor tab finished compiling its React component tree, the local storage retrieval function returned null. The storage key was nowhere to be found.
Here is the exact dispatch code responsible for initiating the handoff before our fix:
export function queueEditorHandoff(payload: EditorHandoffPayload): string {
  const id = `handoff_${Date.now()}_${Math.random().toString(36).slice(2, 8)}`;
  const storageKey = `yellorn_handoff_${id}`;

  window.localStorage.setItem(storageKey, JSON.stringify(payload));

  const targetUrl = new URL("/", window.location.origin);
  targetUrl.searchParams.set("handoff", id);

  const opened = window.open(targetUrl.toString(), "_blank", "noopener");
  if (!opened) {
    window.localStorage.removeItem(storageKey);
    throw new Error("Popup blocked by browser. Please allow popups.");
  }
  return id;
}
At first glance, this implementation looks defensive and responsible. It stores the payload, opens the target window with modern isolation flags to guard against reverse tabnabbing attacks, and checks whether the window opened successfully to clean up leftover entries if a popup blocker intervened.
Yet this defensiveness contained a fatal flaw. When the user clicked the button, the browser opened the new tab without friction. But in the very next microtask of the sender tab, an error threw, executing window.localStorage.removeItem(storageKey) immediately. The payload was expunged before the target tab even finished resolving its first network bundle.
Part 3: Diagnosis (The Rough Edges)
Why was the opened variable falsy when the tab clearly appeared on screen? The answer resides in Section 7.4.2 of the WHATWG HTML Living Standard specification.
When one page launches another using script navigation, the child tab retains an active reference to its initiator through the window.opener property. This property carries real security risks: malicious pages in child tabs can rewrite the parent window URL to display phishing pages without warning. To neutralize this vulnerability, developers pass the "noopener" flag.
However, the HTML specification defines an explicit side effect: whenever the "noopener" keyword appears in the window features argument, the browser must sever all browsing context links and return null unconditionally.
HTML Living Standard § 7.4.2:
If the window features contain the token "noopener",
the return value of window.open() MUST be null.
Consequently, calling window.open(url, "_blank", "noopener") always yields null in compliant modern browsers, whether the popup succeeded or was blocked. The defensive check mistook this intentional security behavior for a popup failure, panicked, and triggered premature cleanup that doomed the receiving tab.
Compounding this issue was a second architectural quirk inside the visualizer layout engine. Even when the payload survived, the ComfyUI format metadata registered its available views in the order ["tree", "graph"]. Because the visualizer context defaulted to the first element in the array, incoming workflows booted into a static tree inspector instead of the graphical flow canvas.
Part 4: Resolution (Decision Matrix)
Resolving this failure required three coordinated fixes: decoupling popup verification from opener isolation, introducing safe expiration windows, and setting the graph view as the primary default.
First, we stripped "noopener" from the window.open feature string. This allows the call to return an authentic WindowProxy reference so the popup blocker check functions accurately. Immediately after confirming the window exists, we break the opener link manually:
// Production fix: accurate blocker detection with zero spec nullification
export function queueEditorHandoff(payload: EditorHandoffPayload): string {
  const id = `handoff_${Date.now()}_${Math.random().toString(36).slice(2, 8)}`;
  const storageKey = `yellorn_handoff_${id}`;

  window.localStorage.setItem(storageKey, JSON.stringify(payload));

  const targetUrl = new URL("/", window.location.origin);
  targetUrl.searchParams.set("handoff", id);

  const opened = window.open(targetUrl.toString(), "_blank");
  if (!opened) {
    window.localStorage.removeItem(storageKey);
    throw new Error("Popup blocked by browser. Please allow popups.");
  }

  // Sever the security link without triggering spec nullification
  opened.opener = null;
  return id;
}
Second, we introduced a 30-second expiration window in storage, preventing immediate deletion on race conditions. Once the target tab mounts and consumes the data, it purges the entry and calls window.history.replaceState to strip ?handoff= from the URL bar, ensuring a clean address bar and avoiding duplicate processing on page reloads.
| Handoff Strategy | Core Architectural Advantage | Primary Operational Limitation |
|---|---|---|
| LocalStorage Ticket (Chosen) | Clean context separation, handles large payloads | Restricted to identical origin domain |
| BroadcastChannel API | In-memory pub-sub with zero disk overhead | Fails when destination tab is not yet mounted |
| Window.postMessage | Works across distinct origins and iframes | Vulnerable to startup race conditions |
| URL Search Parameters | Completely stateless without storage dependency | Hard ceiling at 2KB URL length limits |
Finally, inside the ComfyUI metadata configuration, we flipped the view priority array to ["graph", "tree"]. Clicking the inspect button now triggers the ReactFlow canvas directly, laying out every node, model weight, and sampler connection immediately.
Final Take
Never assume standard DOM methods behave intuitively when combined with modern browser security flags. A single feature string can invert return values and silently destroy production state pipelines.
Student First Assignment
Open your browser developer console and execute these two small experiments:
// Test 1: Observe spec nullification with noopener
const win1 = window.open("https://example.com", "_blank", "noopener");
console.log("Win1 return value:", win1); // Always logs null!

// Test 2: Observe safe manual detachment
const win2 = window.open("https://example.com", "_blank");
if (win2) {
  win2.opener = null;
  console.log("Win2 reference retained and secured:", !win2.closed);
}
Notice how win2 provides a genuine reference for health checks while maintaining isolation. Test this pattern in your own multi-tab workflows.
Frequently Asked Questions (FAQ)
Why does window.open with noopener return null?
The HTML Living Standard dictates that returning null guarantees complete contextual isolation, preventing the initiator tab from accessing properties or dispatching events into the newly created browsing context.
Why not use BroadcastChannel for tab handoff?
BroadcastChannel requires the destination tab to be already open and actively listening to the channel. When launching a new tab, the receiver needs hundreds of milliseconds to boot and parse scripts, completely missing early broadcast messages.
Is setting window.opener to null as secure as noopener?
Yes. Explicitly severing the property prevents the child tab from referencing the parent window, neutralizing reverse tabnabbing attacks while allowing the sender to verify that the popup launched successfully.
Related posts
- AI & Agents
Fulfill Your Dirty Fantasies with ComfyUI: Uncensored Workflow Guide
Step-by-step engineering guide to running uncensored ComfyUI workflows locally on NVIDIA GPUs. Master node graphs, bypass cloud filters, and optimize VRAM.
22 min readRead → - AI & Agents
Ego Lite: What It Is, How It Works & AI Browser Agent Setup Guide
What is Ego Lite? Guide to the Ego Lite browser and ego-browser skill for Claude Code and Cursor to automate the web using your real logged-in cookies.
15 min readRead → - AI & Agents
High-Leverage Coding Terms & Jargon for AI Coding Agents
Discover the architectural keywords and high-leverage engineering jargon that turn AI coding agents into precision tools, eliminating hallucinations.
9 min readRead → - Developer Tools
authentik Explained: IdP, SSO, SAML, OAuth2/OIDC, Okta, and Auth0
A smooth primer on authentik, IdP, SSO, and login protocols that turns identity-management jargon into a usable mental model.
12 min readRead →